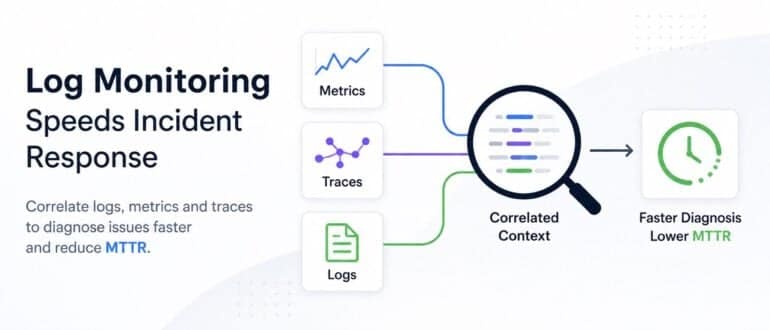
Why Log Monitoring Is the Missing Link in Most Incident Response Workflows
Modern engineering teams have invested heavily in observability. Dashboards are populated, alerts are configured, on-call rotations are set. Yet when
Devops updates
Modern engineering teams have invested heavily in observability. Dashboards are populated, alerts are configured, on-call rotations are set. Yet when
CISA just gave software supply chain security a long-overdue refresh. Working with the NSA, the FBI, and a roster of
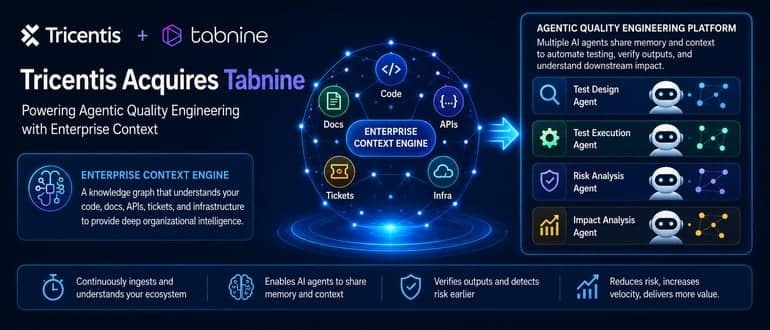
Tricentis today revealed it is acquiring Tabnine to gain access to a knowledge graph that will be used to provide

The gap between how fast AI writes code and how reliably teams verify it is quietly becoming a balance-sheet risk.
Not long ago, some business leaders seemed to view enterprise search as a “nice-to-have.” Or, at the very least, they
OpenAI has released its Codex Security command-line interface and software development kit as open source software under the Apache 2.0
Most enterprises never fully finished the DevOps transformation they started a decade ago. Agentic coding is now surfacing every place
AI coding tools are producing more code, faster, than teams have ever had to absorb before. That productivity story is

Las Vegas, USA, July 29th, 2026, CyberNewswire Catches rogue AI agents – and stops them in live production before they
DevOps used to be a manageable rhythm: several core tools, a handful of respected blogs, and a few incident write-ups