
OWASP Adopts CVE Lite CLI to Boost Dependency Scanning
Checking for dependency vulnerabilities in freshly developed software is usually done near the end of the build process. Remediation at […]
Checking for dependency vulnerabilities in freshly developed software is usually done near the end of the build process. Remediation at […]
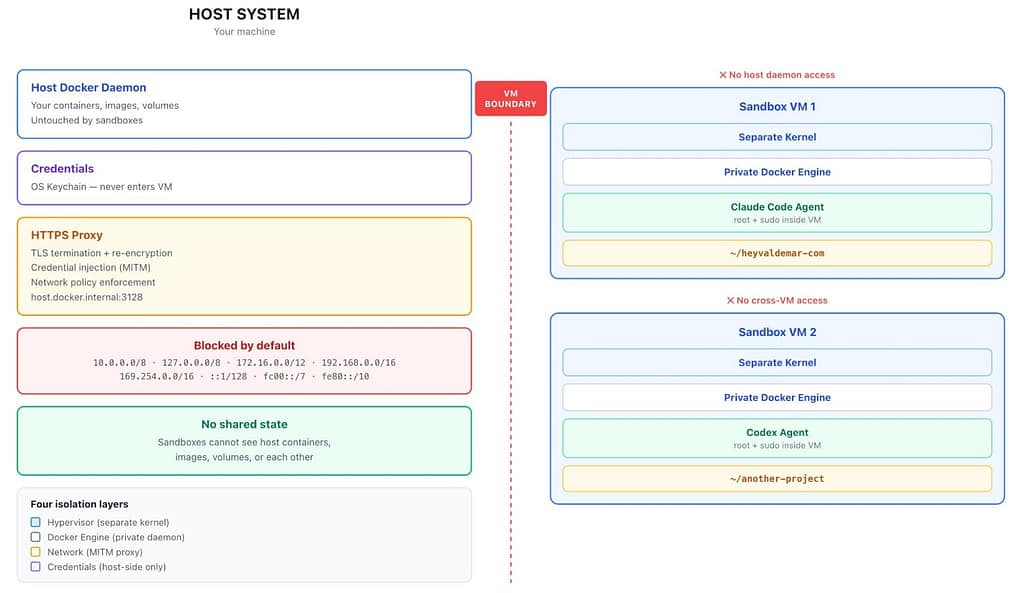
Earlier this year I mass-migrated my blog to Astro using Claude Code. 146 posts. 6,024 images. Canonical URLs, JSON-LD markup,

As AI capabilities continue to evolve, AI is becoming central to managing the growing complexity of distributed, hybrid enterprise environments,

The moment you push your code, deployment fires off on its own. The pipeline kicks in, the tests sail through,

A dangerous vulnerability found in Anthropic’s popular Claude Code developer model could have allowed bad actors to grab control of

Modern engineering teams ship software faster than ever, but this velocity often comes at the cost of security. Vulnerabilities frequently

DevOps teams don’t have a firewall problem; they have an identity problem. When you consider the recent security incidents in cloud-native environments,

In 2026 and beyond, AI will not just change how software is developed, but change the very fundamentals of how

The Model Context Protocol (MCP) has made it much easier to connect tools and resources to AI applications. But once
We’re in the process of significantly improving memory safety in C#. The unsafe keyword is being redesigned to inform callers