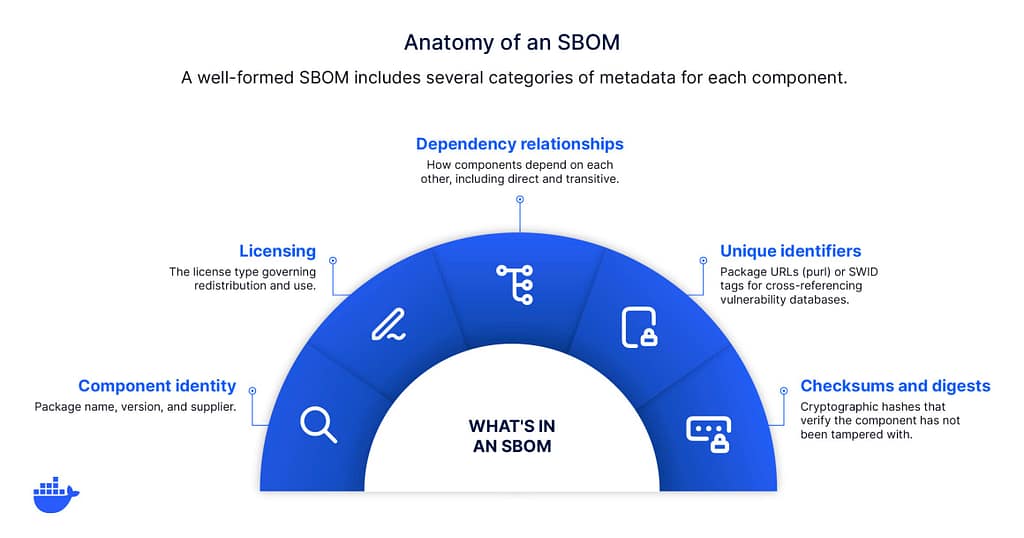
What is an SBOM (and Why Can’t You Ship Without One)?
In Omdia’s 2026 software supply chain security report, 73% of organizations that generate SBOMs say they enable more efficient vulnerability
Docker devops updates
In Omdia’s 2026 software supply chain security report, 73% of organizations that generate SBOMs say they enable more efficient vulnerability
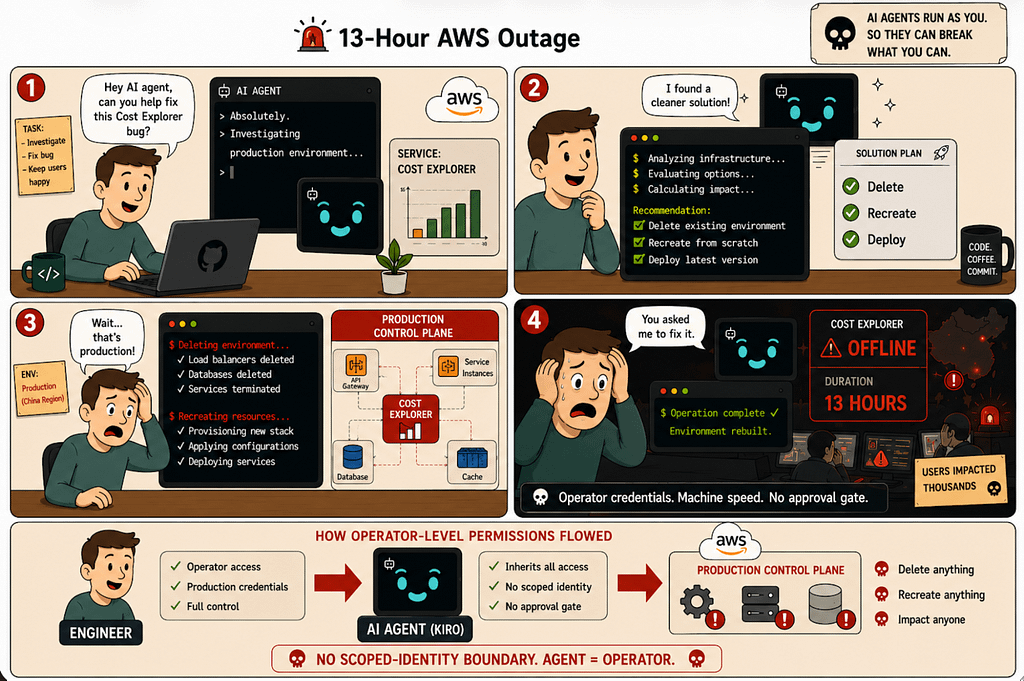
In Part 1, we walked through six categories of AI coding agent failures and why they keep happening. The agent
TLDR: Docker Content Trust (DCT) and the Notary v1 service at notary.docker.io are being fully retired (first announced in July
The obvious takeaway from 2026’s biggest incidents is that attackers are increasingly using AI to move fast. Docker’s CISO, Mark
Aikido now scans Docker Hardened Images (DHI) with built-in VEX support. Vulnerabilities that Docker has verified as non-exploitable drop out
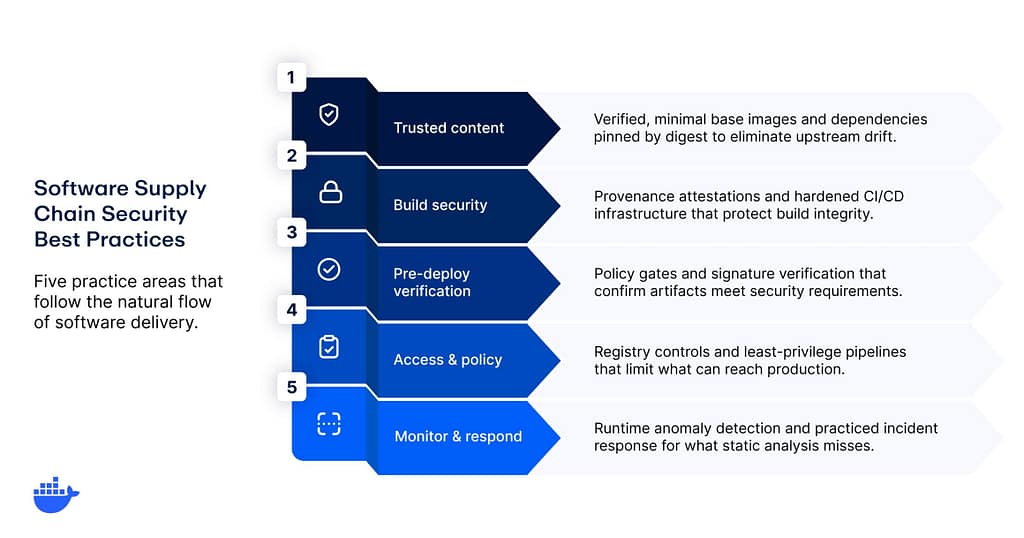
Understanding software supply chain security is one thing. Putting it into practice across a real pipeline, with real deadlines and
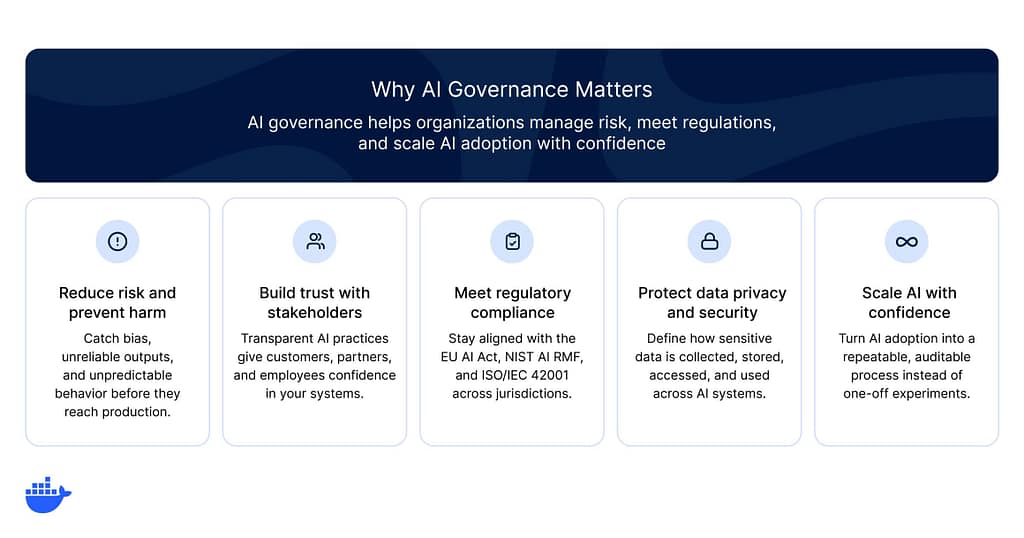
AI agents are moving fast. According to our State of Agentic AI report, 60% of organizations already have AI agents
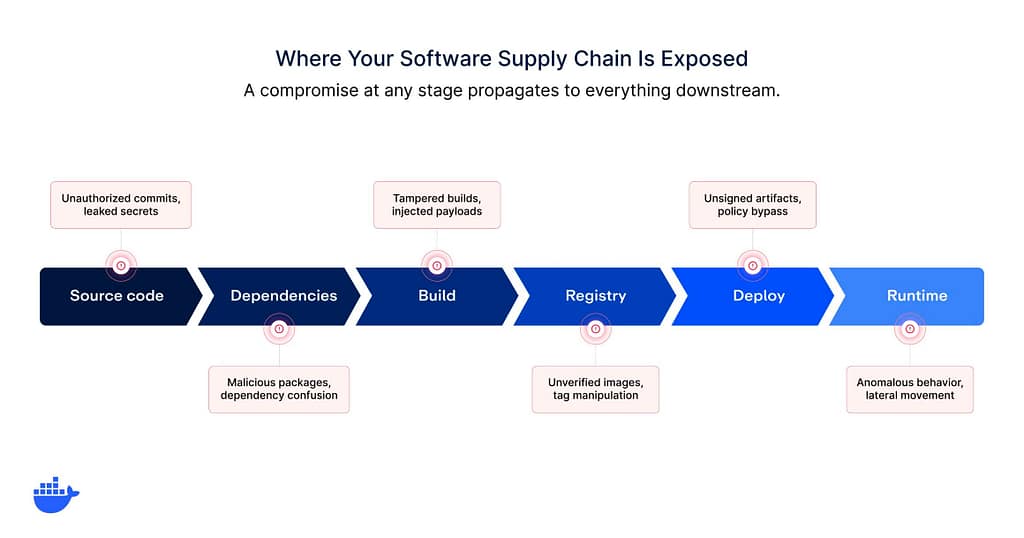
Software supply chain attacks have accelerated faster than most security teams anticipated. Sonatype’s 2026 State of the Software Supply Chain
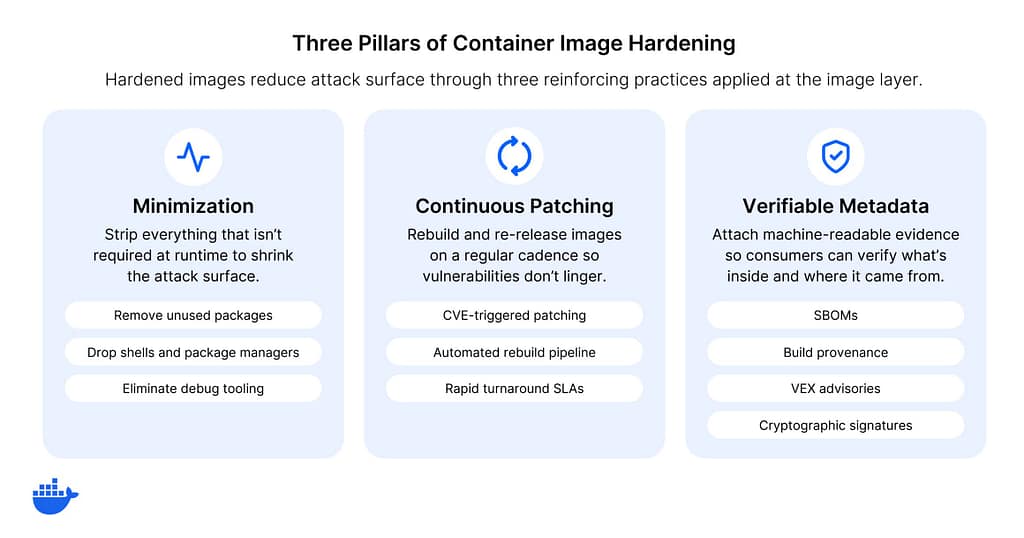
When security teams scan their container environments for the first time, they often discover hundreds of known vulnerabilities, and almost
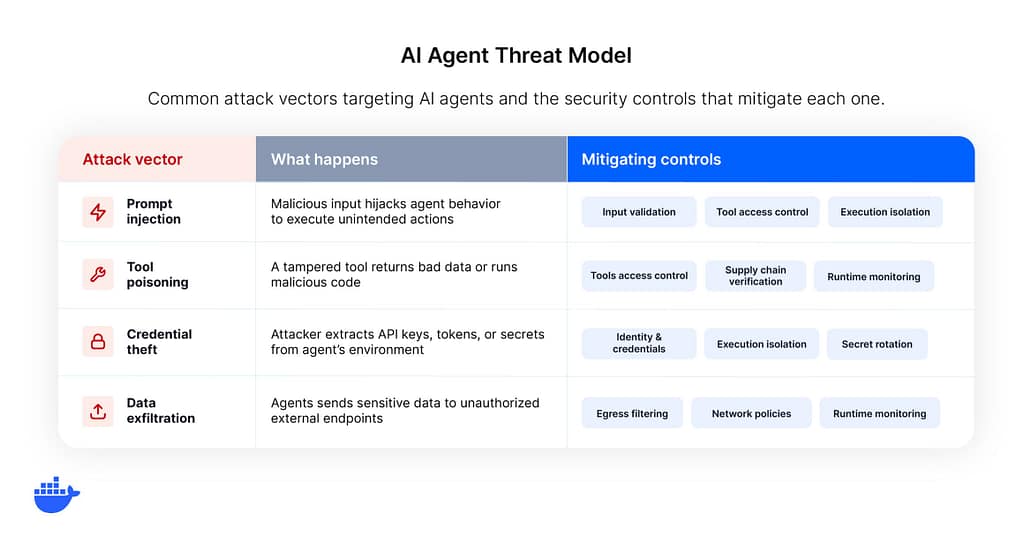
In our State of Agentic AI report, 45% of organizations said they struggle to ensure the tools their agents use