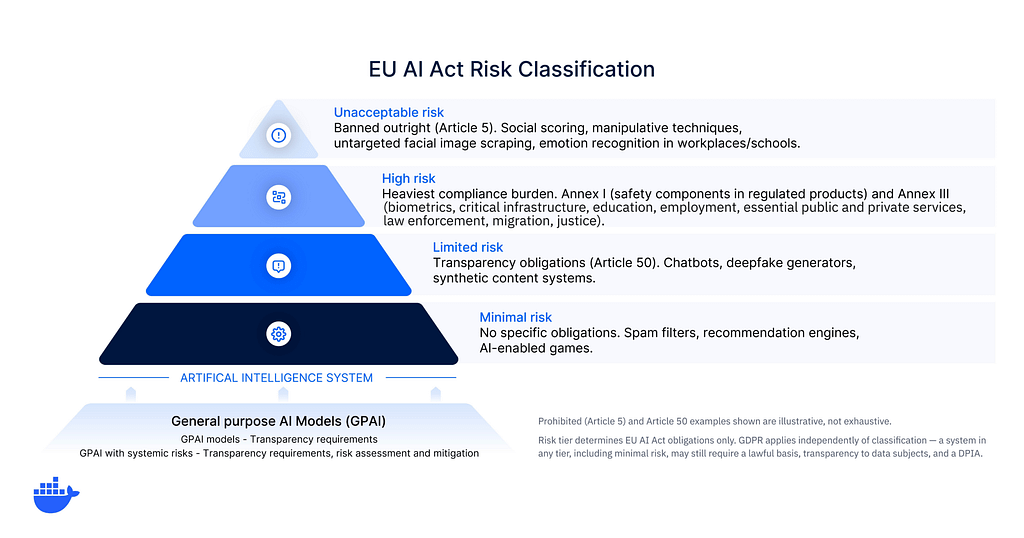
What Does EU AI Act Compliance Require?
For teams building AI-governed systems, the EU AI Act adds compliance obligations to every stage of the development lifecycle, from […]
Docker devops updates
For teams building AI-governed systems, the EU AI Act adds compliance obligations to every stage of the development lifecycle, from […]

According to Omdia’s 2026 software supply chain security report, 86% of organizations find SBOM generation challenging. A major driver is

The EU Cyber Resilience Act (CRA) was officially introduced on December 10th 2024, to protect foundational EU values in the
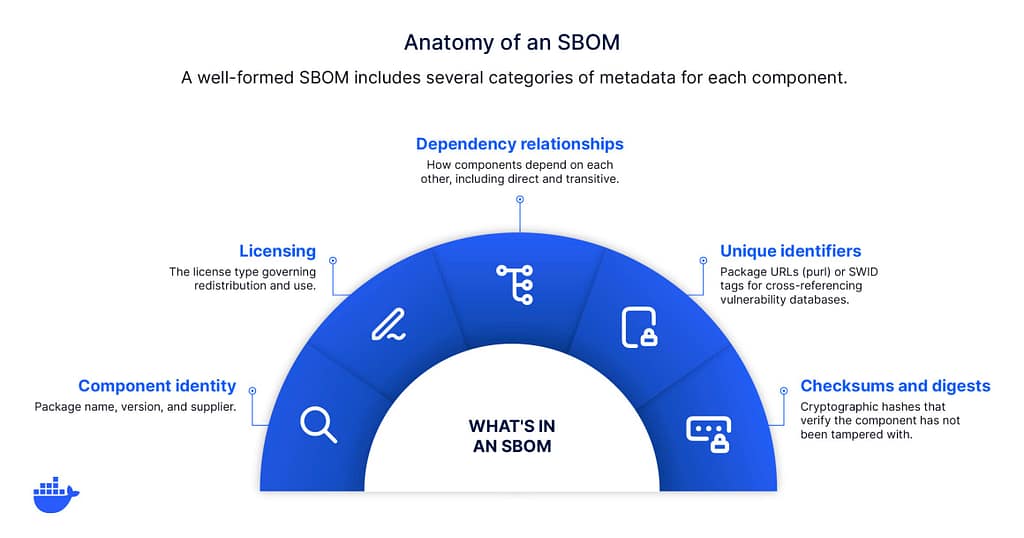
In Omdia’s 2026 software supply chain security report, 73% of organizations that generate SBOMs say they enable more efficient vulnerability
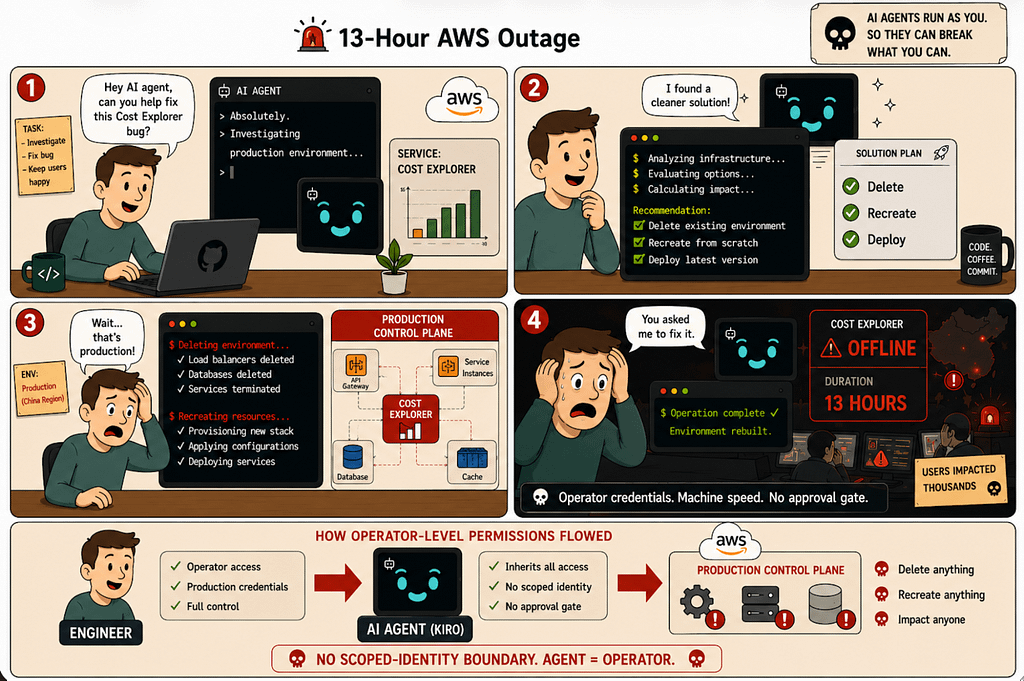
In Part 1, we walked through six categories of AI coding agent failures and why they keep happening. The agent
TLDR: Docker Content Trust (DCT) and the Notary v1 service at notary.docker.io are being fully retired (first announced in July
The obvious takeaway from 2026’s biggest incidents is that attackers are increasingly using AI to move fast. Docker’s CISO, Mark
Aikido now scans Docker Hardened Images (DHI) with built-in VEX support. Vulnerabilities that Docker has verified as non-exploitable drop out

Understanding software supply chain security is one thing. Putting it into practice across a real pipeline, with real deadlines and

AI agents are moving fast. According to our State of Agentic AI report, 60% of organizations already have AI agents