Why Your CI/CD Pipeline Is Your Most Unprotected Attack Surface
Your team probably spends considerable effort securing your application. WAFs, rate limiting, input validation, penetration testing. Then code passes through
Devops updates
Your team probably spends considerable effort securing your application. WAFs, rate limiting, input validation, penetration testing. Then code passes through
The debate isn’t new — but the stakes are. In 2026, the gap between companies that get this decision right

Anyone who has run more than one Claude Code session at a time on the same codebase already knows the

Anthropic announced it has redesigned Claude Projects to coordinate multiple coding sessions in parallel, with the new experience debuting in

StackHawk this week launched Wingman, an artificial intelligence (AI) tool that makes it possible for application developers to automatically fix

Harness today previewed a revamped user interface for its platform for managing software deployments that makes it simpler for software
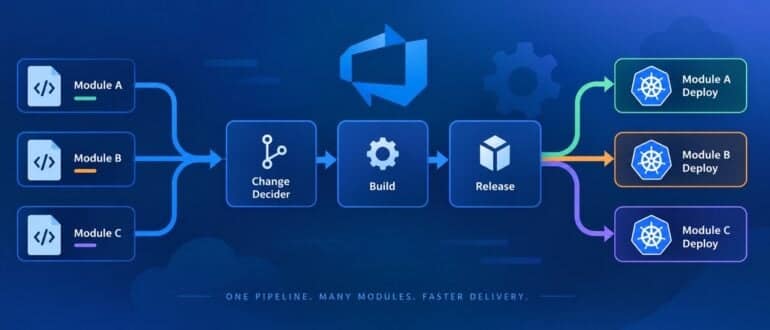
Two modules in a repository had near-identical Azure DevOps build and release definitions. A third would have required another pair.

Splunk is gearing up to make an artificial intelligence (AI) model for analyzing log data available on Hugging Face under

DevOps teams have spent years adding testing, logging, secrets management and auditability to software delivery pipelines. ML pipelines deserve the

For teams already using Django, Django-Bolt offers a way to improve API performance without switching to another framework. It keeps